

 2
Microsoft and Coinbase helped dismantle EvilTokens, an AI phishing service tied to more than 12,000 compromised inboxes worldwide.
The operation had reached more than 10,000 organizations within months of launching, spanning financial services, real estate, healthcare, construction and other industries, Microsoft said.
The company and its partners seized 50 websites used by EvilTokens and disabled more than 150 related domains, while UK police arrested two men on Sept. 11 on suspicion of offenses connected to the alleged operation. Police later released both on conditional bail.
EvilTokens' phishing service relied on AI use
EvilTokens had packaged much of the business-email-compromise process into a subscription service sold through Telegram. Microsoft said customers paid a $1,500 initiation fee and $500 recurring subscription for tools that combined account compromise, mailbox access, reconnaissance, and AI-assisted fraud preparation in a single interface.
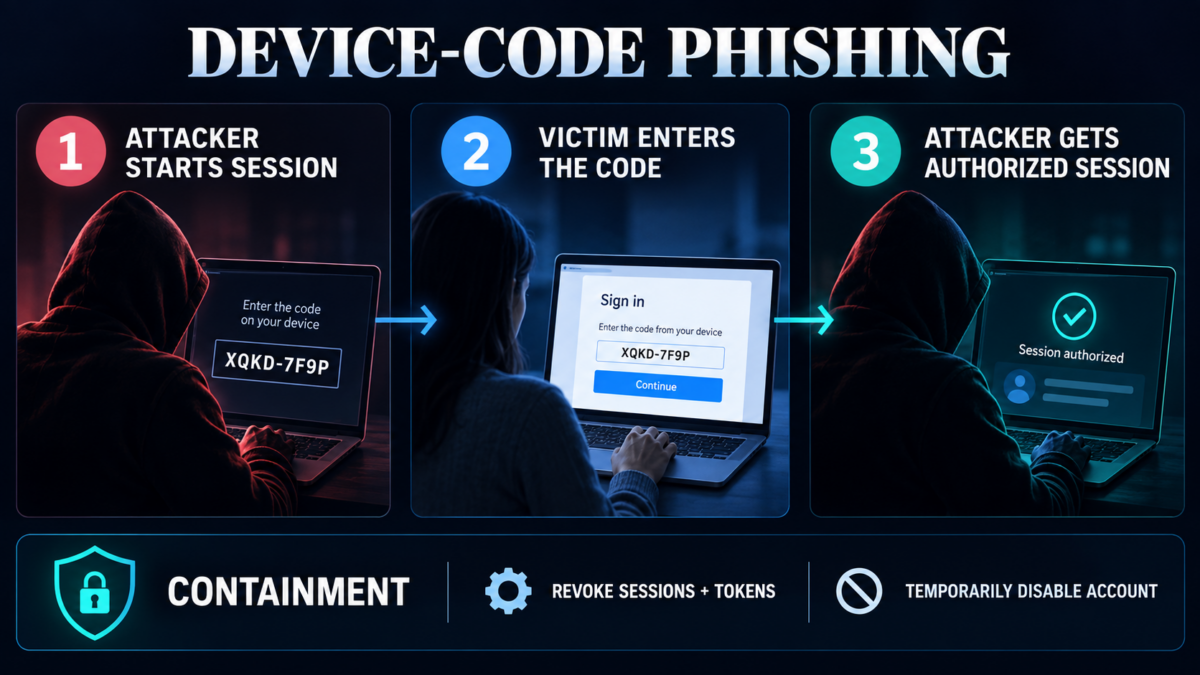
The service’s entry point relied on Microsoft’s device-code authentication, a legitimate sign-in flow designed for hardware such as smart TVs and conferencing equipment that cannot easily support standard browser logins.
Attackers initiated the authentication request themselves, then sent the resulting code to targets through phishing emails disguised as invoices, shared files, and other routine business communications.
Victims who entered that code on Microsoft’s legitimate website effectively approved the session waiting on the attacker’s device.
The process could still require a password and multifactor authentication when the user was signed out, but those credentials remained on Microsoft’s infrastructure. The process generated authorization for the attacker-initiated session.
That gave EvilTokens something more useful than a stolen password: an authenticated foothold inside the mailbox. The platform then automated work that has traditionally required attackers to spend hours reading correspondence and reconstructing how an organization moves money.
Its AI tools could translate and summarize messages, identify reporting lines and trusted contacts, surface pending invoices and wire-transfer conversations, and determine which employees had authority over payments.
Microsoft said preset prompts could identify an organization’s “money movers” and recommend people to impersonate, letting customers move from account access to targeted fraud with far less manual reconnaissance.
Investigators also found evidence that parts of EvilTokens were built with AI-assisted coding tools, lowering the technical burden on both sides of the operation.
The result was a service that could help less-skilled customers gain access to an account, understand its contents, and prepare an impersonation campaign without assembling each capability separately.
Crypto payments gave investigators a trail
The subscription model also created the financial trail Coinbase used to work backward through the operation.
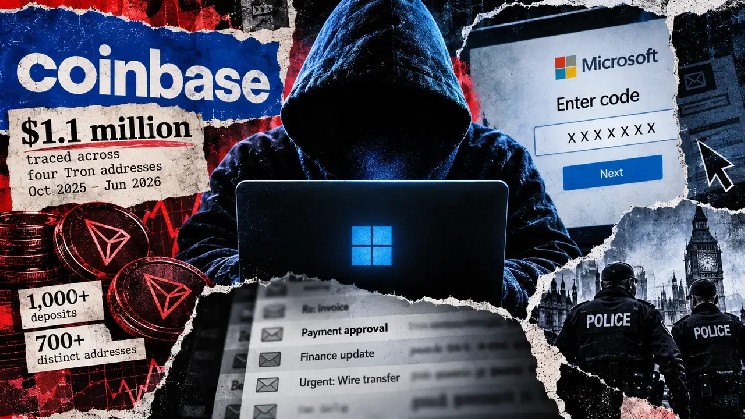
Coinbase’s Global Intelligence team traced about $1.1 million in EvilTokens platform revenue across four Tron addresses between October 2025 and June 2026. It identified more than 1,000 deposits from over 700 distinct addresses and mapped flows from payments into EvilTokens through their eventual cash-out destinations. The figures represent revenue paid to the service rather than the amount ultimately stolen from phishing victims.
Coinbase said it combined transaction data with merchant records, device information and open-source intelligence to help attribute the platform to its alleged operators before referring the matter to London’s Metropolitan Police.
The exchange also investigated EvilTokens purchasers it identified on its own platform and referred those cases to law enforcement. Its evidence contributed to Microsoft’s civil action against the service.
Coinbase customers were also among those caught downstream. The exchange said some users were manipulated through compromised email conversations into sending cryptocurrency to scam-controlled addresses. Coinbase accounts and credentials were not compromised.
The disruption interrupted an operation that was already looking beyond Microsoft. Coinbase said EvilTokens’ operator had signaled plans to extend the toolkit to Gmail and Okta accounts, potentially spreading the same model across other identity platforms.
Microsoft warned that removing the service’s current infrastructure would not eliminate the method. The company recommends organizations block device-code authentication where it is unnecessary and tightly restrict it where operationally required. For accounts suspected of compromise, it advises revoking refresh tokens, forcing reauthentication and, in some cases, temporarily disabling the account.
That last step can carry a short-term operational cost, but Microsoft said standard session revocation may leave existing access tokens usable for up to an hour. Attackers have exploited that window in recent campaigns, leaving security teams to choose between brief disruption to legitimate users and continued access for someone already inside the mailbox.

 en.cryptonomist.ch
 coinedition.com
 coinfomania.com